KnowAll.ai

KnowAll AI · Continuous AI security

The Purple Team:
break it
before they do.

Attackers now use AI to find holes around the clock. So does the KnowAll Purple Team: Pennie attacks, Ollie defends and fixes, and Poppie runs the loop between them.

KnowAll.ai

The problem

A flood of advisories.
A handful that matter.

566

new CVEs a day — published in the 30 days to 23 Oct 2026. No person can read every one.

88,565

published in 2026 so far (to 23 Oct), against 49,972 in the whole of 2025.

245

added to CISA’s actively exploited list in 2025. The skill is knowing which handful affect your code, and fixing those first.

CVE (Common Vulnerabilities and Exposures): the public ID assigned to a publicly disclosed security flaw. KEV: CISA’s catalogue of flaws attackers are actively exploiting. Sources: NIST NVD; CISA KEV.

KnowAll.ai

Frontier AI on defence

Attackers use AI.
So do we.

Frontier models do the reasoning

Models from Anthropic and OpenAI, via Microsoft Foundry, read your code, judge whether a flaw is really exploitable and write the fix.

Automation filters first

Every new advisory is checked automatically, around the clock, against the exact software your code uses. Only the matches go to the AI, so it never wastes time on flaws that can’t touch you.

Anthropic OpenAI
KnowAll.ai

Meet the team

Red attacks. Blue defends.
Purple makes them one team.

Pennie the Pen Tester
Red team

Attacks like a real adversary, mapped to the OWASP Top 10, the OWASP LLM Top 10 and MITRE ATT&CK.

Ollie the Operator
Blue team

Filters the daily CVE flood down to what affects you using CISA KEV and EPSS, then defends and patches.

Poppie the Planner
Purple lead

Runs the attack, detect and fix loop between them, so red and blue work as one team.

How it works

Attack. Defend. Fix. Report. Repeat.

KnowAll.ai
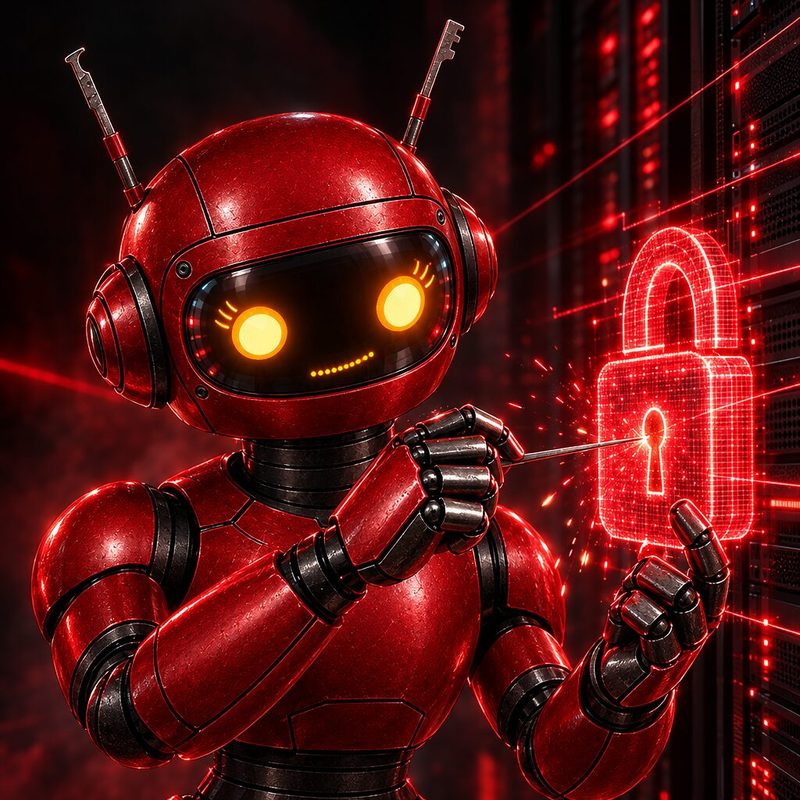
Pennie, the red robot, picking a glowing red holographic padlock on a server rack

Pennie attacks

With your written authorisation, Pennie probes your apps, APIs and cloud, and checks every new CVE against your code to prove what is really exploitable.
Ollie, the blue robot, raising a glowing hexagonal shield against red shards

Ollie defends

Did Ollie see it? He watches your Microsoft Defender for Cloud and Sentinel around the clock, and every attack he missed becomes a new detection.
Ollie, the blue robot, sealing a crack in a glowing panel of code

Ollie fixes

He opens a pull request with the fix and a test that proves it. Your developers review and merge, then Pennie attacks again to confirm it holds.
Poppie, the copper robot, holding a tablet projecting a locked padlock and a rising chart

Poppie reports

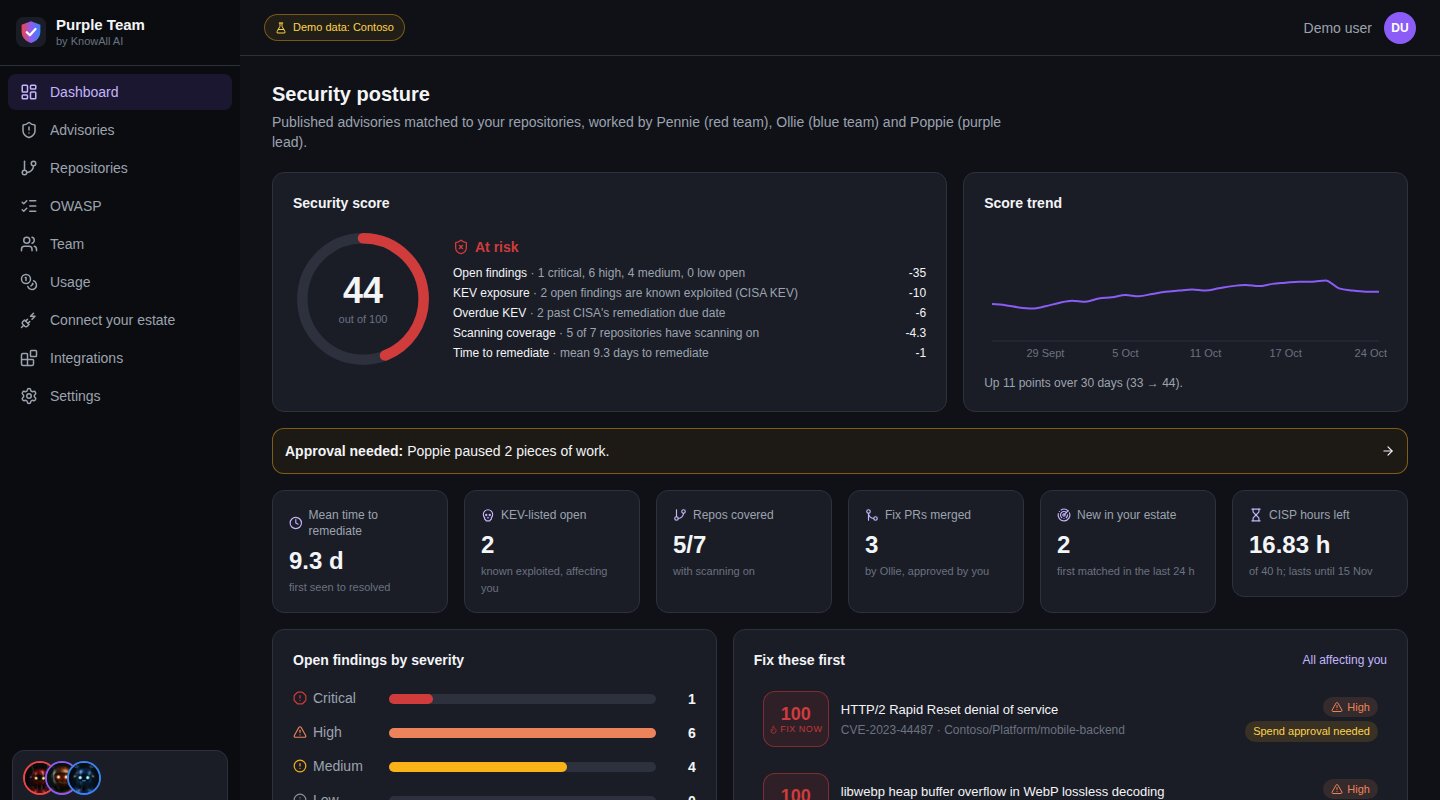
Poppie scopes the work, tracks every finding as a risk, issue or task, and shows your score, time to detect and time to fix each month.

KnowAll.ai

Patch fast

From advisory
to merged fix.

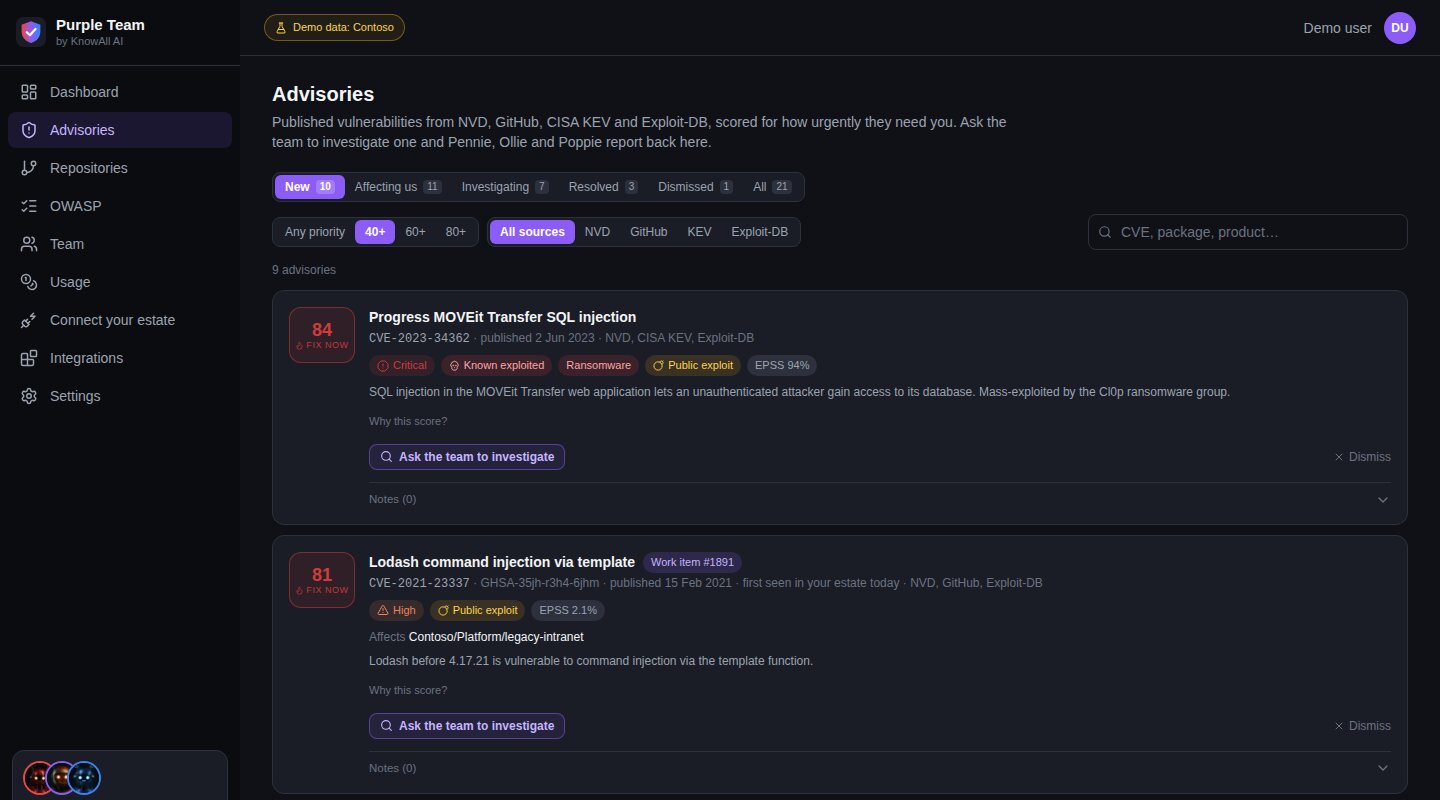
Matched. Every new advisory is checked continuously against the packages you run.

Prioritised. CISA KEV and EPSS put the actively exploited and the likely-next first.

Fixed. Ollie opens a pull request with the fix and a test that proves it.

Merged. Your developers review and merge. Nothing lands without you.

Re-tested. Pennie attacks again to confirm the fix holds.

Time to fix
From advisory published to merged fix
Exploited, still open
Actively exploited issues open right now
KnowAll.ai

Safe by design

Attacked on purpose.
Never by surprise.

Nothing is tested without written authorisation. Targets, timings and rules of engagement are agreed with you first.
Non-destructive by default. Anything risky runs against a staging copy, or is scheduled with you.
Every fix goes through your existing review process. A pull request with a proving test; you merge it.
Private until the fix ships. On public repos, new flaws go through a private GitHub Security Advisory, never a public issue.
KnowAll.ai

Nothing new to install

Works with what
you already run.

GitHub
Azure DevOps
GitHub Advanced Security
Dependabot
Renovate
CodeRabbit
ZAP
Nuclei
Defender for Cloud
Microsoft Sentinel
Azure Lighthouse
Microsoft Entra ID
Microsoft Foundry
Microsoft Azure

Hover over a logo to see what it does.

Your Purple Team Portal

What you see, every month

KnowAll.ai
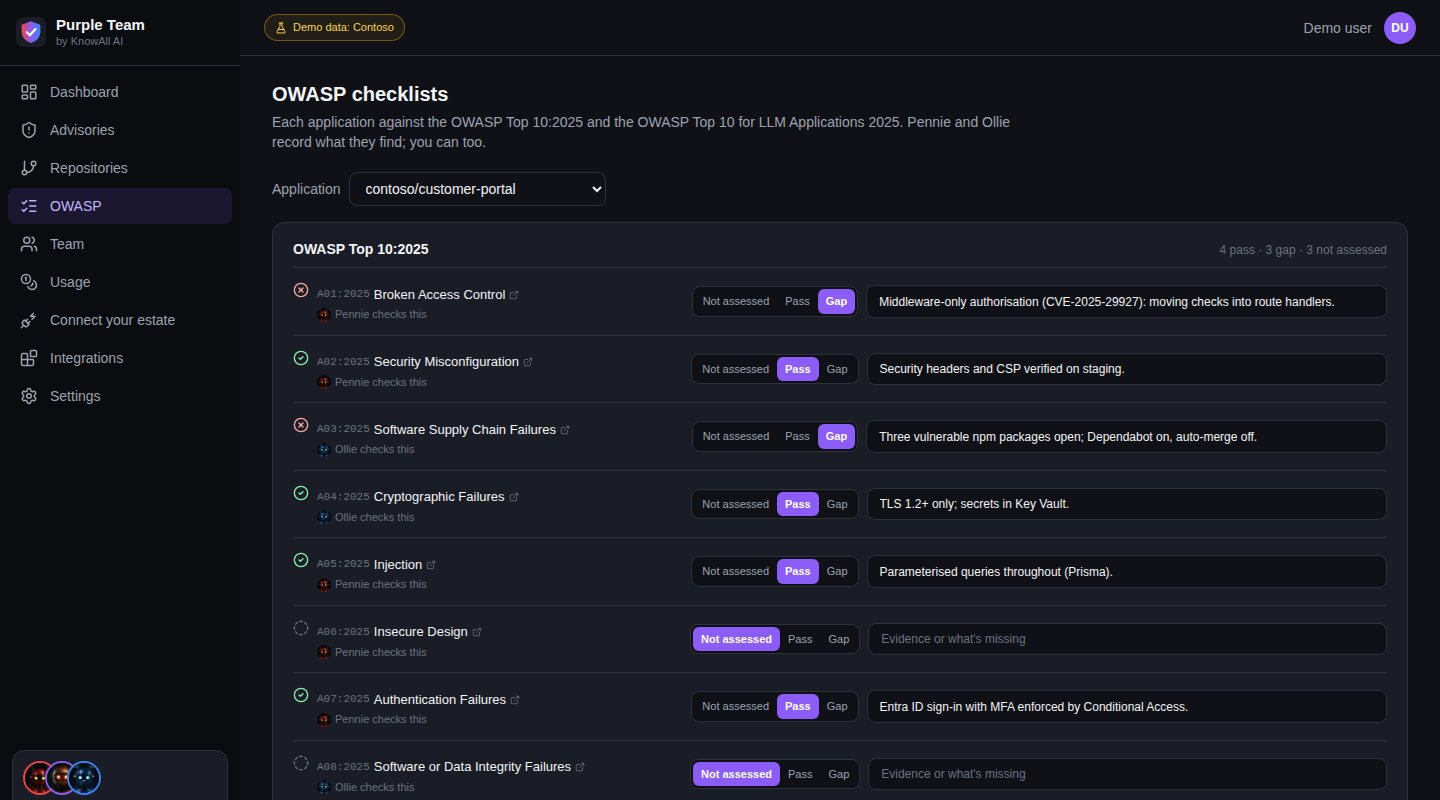
Your security score, and how it moves month by month.
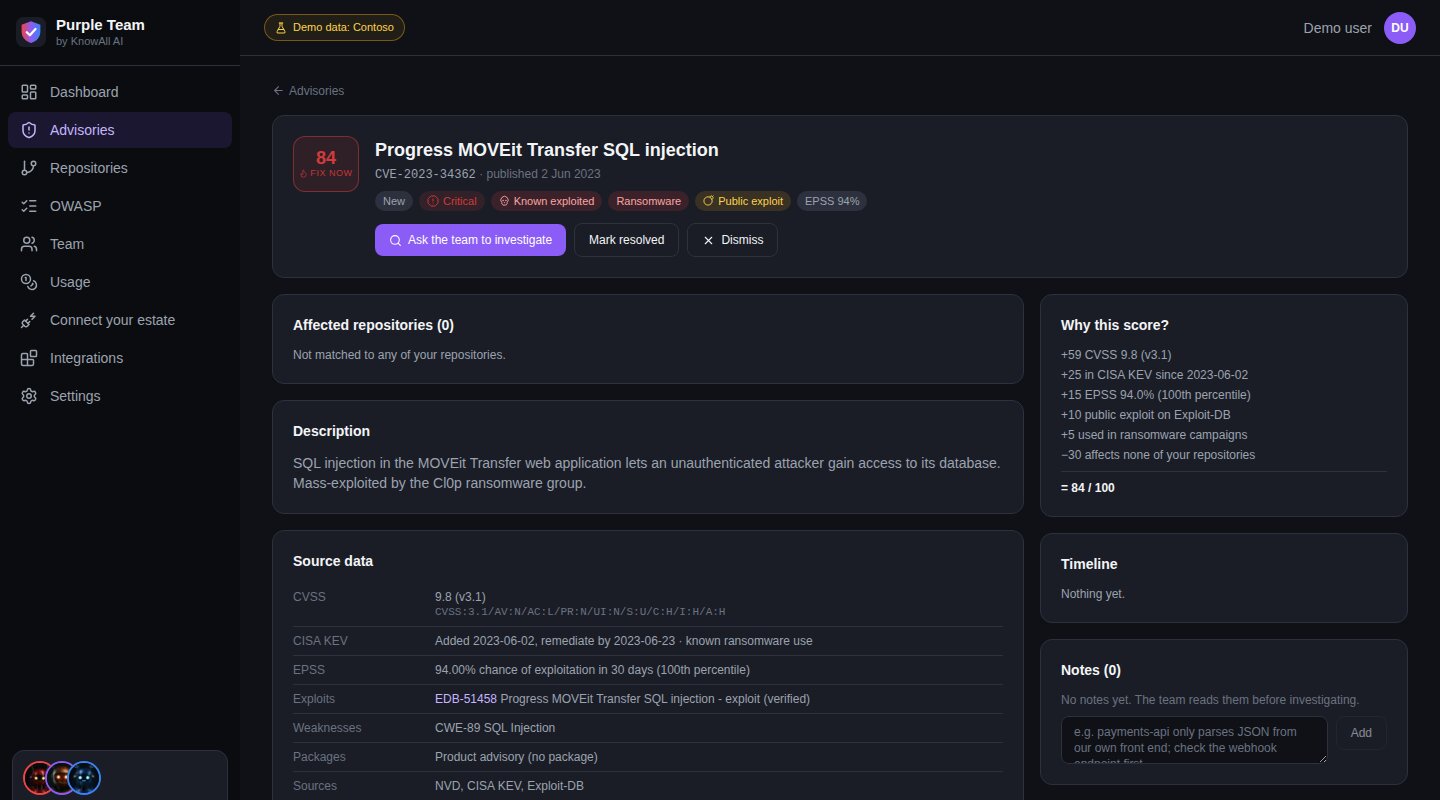
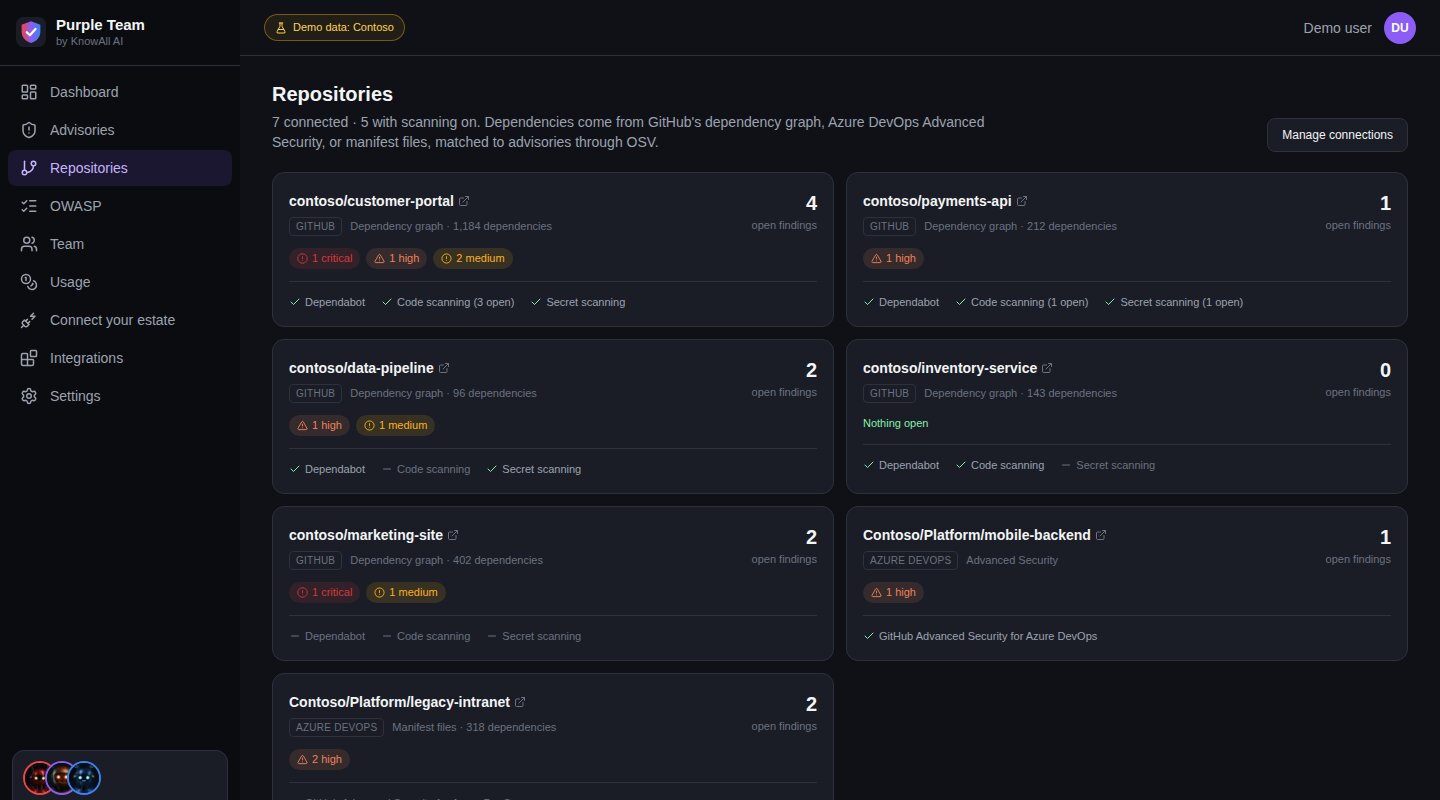
Every advisory that affects you, matched to your repositories.
What we did about each one, from first seen to merged fix.
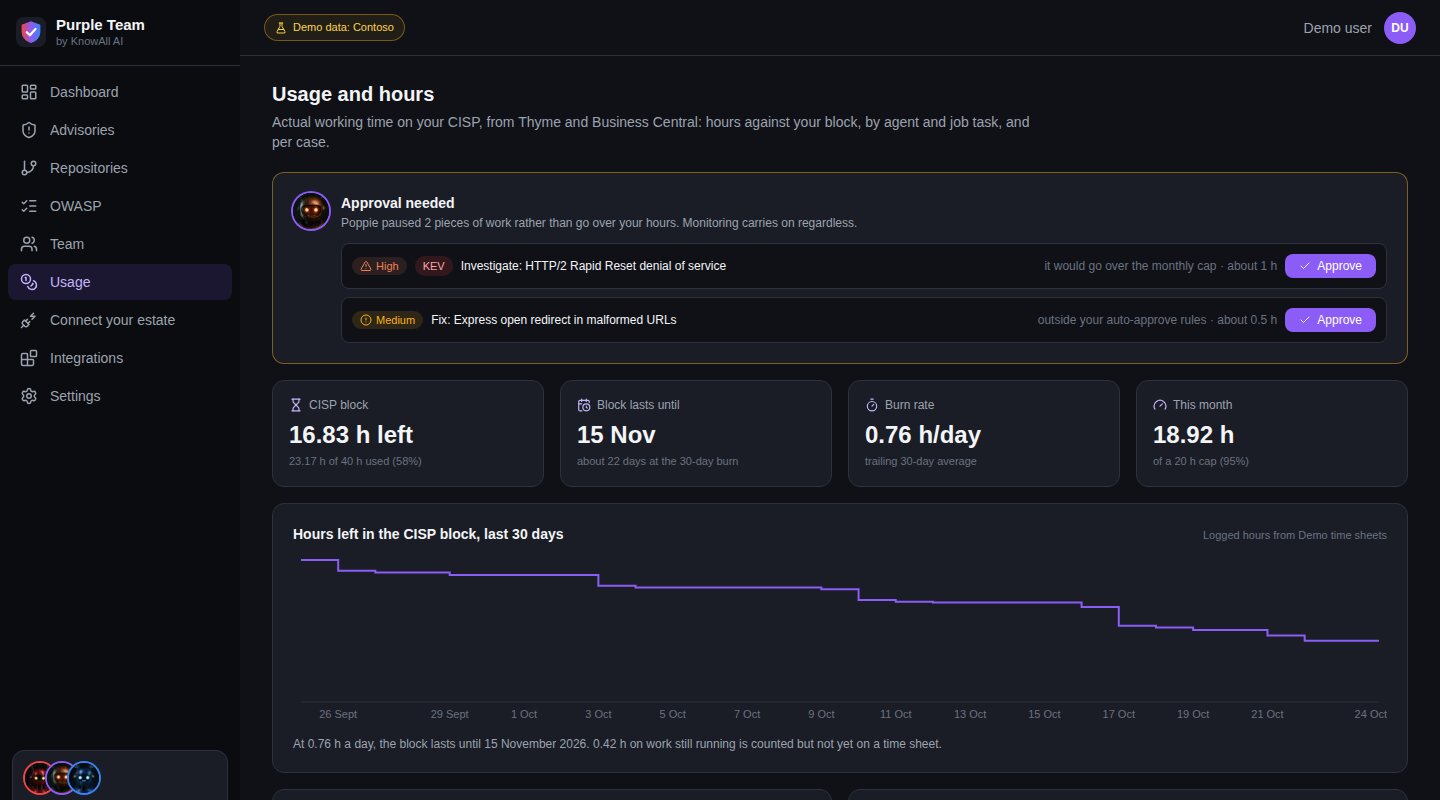
Time spent per case, so every hour billed is accounted for.
KnowAll.ai

Three ways to run it

Your data,
where you want it.

Hosted

We run the team and your portal for you. Fastest to start.

In your tenant

Your data stays in your Azure. Our agents work on it.

Fully sovereign

Agents and models run in your Azure too. Nothing leaves.

KnowAll.ai

How you pay

Real hours.
A cap you set.

Security Discovery

Measures your estate: the repositories, cloud and apps in scope, and what is already exposed. Sets your starting score and proposes a monthly budget.

Hours on a CISP

Agents bill the real hours they work on a Continuous Improvement Service Plan, new or existing, with a monthly cap Poppie will not exceed without asking you.

Monitoring

A flat monthly rate keeps Ollie watching Defender and Sentinel, and the matching running, around the clock.

Break it before
they do.

KnowAll.ai

Start with a Security Discovery — we measure your estate, set your starting score and come back with a scoped plan: what Pennie would test, what Ollie would watch, and what your first month’s report would show.

Book a Security Discovery